

Збирач потоків
У кого питали, коли не було Гуглу?

Університетська книгозбірня має в своєму фонді численні книжкові пам'ятки та унікальні старовинні видання, знайомство з якими часто викликає захоплення і подив. Серед них – довідники, енциклопедії, словники, промислові каталоги ХІХ – першої половини ХХ ст.
DIY AI voice assistant with ESP32 and animated OLED eyes
This project builds a complete DIY AI voice assistant on an ESP32 board. The system listens with an I2S microphone, records the voice, transcribes it with the OpenAI Whisper API, generates a response with GPT, and plays it back through an amplifier and speaker. An OLED display animates two expressive eyes that follow the state of the conversation. Everything runs on a standard ESP32, with no complex additional hardware.
jayesh_nawani’s Hackster.io page collects all the project details. The build requires common components: an ESP32 development board, a MAX98357A amplifier, a 0.96-inch OLED display, an I2S microphone, and a 3W speaker. For those who want to start with a ready-made base, the ESP32-C6-Zero board offers a compact and modern alternative, even though the original project uses the classic Development Board.
How the main loop worksThe main loop continuously listens to the I2S microphone. When it detects a sustained volume peak above the threshold of 1000, it starts recording. Recording continues until silence lasts at least 200 ms per 1000 ms of hold, or up to a maximum of 2 seconds. The audio clip is then packaged as a WAV file and sent to the Whisper API for transcription.
The transcription goes to the GPT Chat Completions API, which generates a conversational response. The text is then sent to the TTS API, and the resulting PCM audio is streamed to the I2S amplifier as it arrives. Sampling happens at 16000 Hz, while TTS works at 24000 Hz. The chunk size is 512 bytes, with a speech synthesis rate set to 0.85.
 ESP32 development board (photo: jayesh_nawani)
The OLED display runs a separate FreeRTOS task on core 0, dedicated to animating the eyes and showing the system status. The main pipeline instead runs on core 1. This separation prevents blocking HTTP calls from slowing down the animation. The result is a smooth and responsive interface, with eyes that move while the assistant listens and responds.
The most interesting technical challengesThe project tackles real problems that every maker encounters. Heap fragmentation is one of the toughest: every call to the OpenAI APIs requires contiguous memory. The code frees a 32KB block before each request, so the HTTP libraries have enough space. Without this precaution, calls fail randomly.
Handling blocking HTTP calls is another challenge. On an ESP32, a request to an API can block the main loop for seconds. The adopted solution uses both cores: one for logic, one for animation. In addition, hardware debugging was systematic: each component was tested individually before integrating everything. For example, the microphone was verified with an oscilloscope before connecting it to the amplifier.
For those who want to rebuild the project, the breadboard is the ideal starting point. The connections are simple: the microphone uses GPIO 14, 15, and 32, the amplifier uses GPIO 26, 25, and 22, and the OLED display uses GPIO 21 and 19. A 0.96-inch, 128×64 OLED display like the one in the project is perfect for the animated eyes, thanks to its resolution and high contrast.
 OLED display (photo: jayesh_nawani)
The code uses the Arduino IDE with the ArduinoJson, Adafruit_GFX, and Adafruit_SSD1306 libraries. The trigger threshold is set to 1000, the silence threshold to 200, with a hold of 1000 ms. Three consecutive chunks are needed to validate a minimum sample of 0.6 seconds. These parameters are tuned for a home environment, but can be adjusted easily.
This project demonstrates that a complete AI voice assistant can run on a simple ESP32. No Raspberry Pi or dedicated computer is needed. The combination of Whisper, GPT, and TTS works in real time with acceptable latency. Moreover, the project teaches how to handle concrete problems like limited memory and blocking network calls.
The most fascinating aspect is the OLED display with animated eyes. It adds personality to the device and makes interaction more natural. The dedicated FreeRTOS task shows how to make the most of the ESP32’s two cores. Finally, the project is completely open-source, so anyone can modify and improve it.
- I2S microphone on GPIO 14, 15, 32
- MAX98357A amplifier on GPIO 26, 25, 22
- OLED display on GPIO 21, 19
- Sampling at 16000 Hz, TTS at 24000 Hz
- Trigger threshold 1000, silence 200, hold 1000 ms
- Max recording 2 seconds, chunk 512 bytes
For audio, an open-source amplifier like ANGELO can replace the MAX98357A, offering more flexibility and a modular design. Alternatively, a TDA7297 stereo amplifier is suitable if you want to expand the project to two channels. The choice depends on power needs and available space.
Finally, the project is an excellent starting point for more advanced experiments. You can add recognition of custom commands, integrate a larger display, or connect environmental sensors. The possibilities are endless, and the solid foundation of this project makes every modification easier.
Source: https://www.hackster.io/jayesh_nawani/ai-voice-assistant-with-esp32-4a3d5f
Related productsThe post DIY AI voice assistant with ESP32 and animated OLED eyes appeared first on Open Electronics.
Rohde & Schwarz FSWX-KM700 Adds Pulse Analysis for DRFM Jammer and Radar Testing
DRFM jammers rely on receiving radar signals, digitizing them and retransmitting them with controlled delay, phase and frequency. As radar systems become more agile and use increasingly complex waveforms, test systems need to measure parameters such as pulse shape, timing, modulation and repeatability, as well as analyze complete pulse trains and pulse-to pulse variations. The R&S FSWX signal and spectrum analyzer addresses these requirements with its dual-channel, phase coherent architecture. With the R&S FSWX-KM700 pulse analysis option, Rohde & Schwarz adds a software extension dedicated to pulsed-signal and DRFM analysis, enabling engineers to evaluate pulse parameters, pulse trains, modulation and the timing behavior of jammer signals.
The R&S FSWX-KM700 pulse analysis option measures key pulse parameters, including pulse width, amplitude, rise time, fall time, pulse repetition interval, duty cycle, pulse shape and overshoot. These measurements can help engineers evaluate the accuracy and consistency of reproduced radar pulses and identify variations in timing, amplitude and other pulse characteristics. Such variations can affect the fidelity of a reproduced signal, making accurate pulse analysis important when testing DRFM-based deception and jamming systems.
The analysis also covers complete pulse trains. The option extracts pulse repetition frequency spectra and pulse-to-pulse variation data, allowing engineers to verify complex pulse sequence behavior and timing patterns. R&S FSWX-KM700 supports chirped pulses, pulse width modulation, pulse position modulation and phase-modulated waveforms. Engineers can use these measurements to check whether a device handles modulation schemes used by modern radar systems, including both the pulse envelope and modulation content.
The system can trigger on amplitude, pulse width, pulse repetition interval or user-defined patterns. This helps engineers isolate selected events inside a pulse train and focus the measurement on the relevant parts of the signal. For longer measurements, R&S FSWX-KM700 aggregates results from many captured pulses. This provides information about repeatability and consistency over time and helps engineers assess whether timing or modulation errors occur only under certain conditions.
The option comes with the following displays: parameter trend for DRFM electronic attack technique analysis, capture vs. time to measure jammer response time and latency between stimulus and response, individual pulse parameter display such as pulse amplitude, frequency, and phase to make sure there are no distortions introduced by the jammer. These measurements connect pulse analysis with the behavior of the jammer under test.
With the new R&S FSWX-KM700 option, the FSWX signal and spectrum analyzer gains a more specialized role in DRFM test workflows. It combines phase coherent multi-channel analysis with pulse, pulse train, modulation and segmented capture functions in one instrument, supporting verification of signal fidelity, timing behavior and consistency in agile electronic warfare scenarios.
The post Rohde & Schwarz FSWX-KM700 Adds Pulse Analysis for DRFM Jammer and Radar Testing appeared first on ELE Times.
India’s Semiconductor Market Projected to Reach $200 Billion by 2035: EY-IESA Report
A new analysis report presented by EY-IESA estimates that India’s semiconductor market will grow more than threefold by 2035. It states that the market will increase from nearly $64 billion in 2026 to $200 billion by 2035 covering areas such as artificial intelligence, data centres, telecommunications, electric vehicles, and advanced semiconductor manufacturing.
The findings of the report point to the increase in demand for semiconductors in India’s consumer electronics and industrial sectors. Consumer electronics is the largest demand segment accounting for a 30% market share, followed by Automotive (16%) and Industrial (15%).
Semiconductor imports by India have also increased in recent years. According to the report, semiconductor imports have increased fivefold, from $5.7 billion in FY2017 to $30.3 billion in FY2025, representing a compound annual growth rate of 23%. The report also states that increased domestic demand presents a good opportunity to expand India’s manufacturing, research and development, and supply chain capabilities for semiconductors.
Another key strength is India’s ability in chip design. The country has nearly 20% of the global chip design engineers which is a positive point for talent development and there is a huge opportunity for expand semiconductor manufacturing, chip design and commercialisation.
According to the report, key technologies in the semiconductor industry—including advanced packaging, compound semiconductors, photonics and chip-to-system integration—should be the focus for India’s potential growth. It also calls for stronger semiconductor manufacturing clusters, improved infrastructure, specialised talent and closer industry-academic collaboration.
The Indian semiconductor market, projected $200 billion by 2035, indicates the scale of the opportunity for India as it seeks to expanding its footprints across the semiconductor supply chain.
The post India’s Semiconductor Market Projected to Reach $200 Billion by 2035: EY-IESA Report appeared first on ELE Times.
Vaishnaw Warns India’s Semiconductor Industry of Cyberattacks and Disruptions
As India emerges as a global supplier in the semiconductor industry and builds capabilities in chip design and manufacturing, the country could face cybersecurity, geopolitical, and other disruption-related challenges. Union IT Minister Ashwini Vaishnaw gave this warning during a media interview in New Delhi. While speaking to the media on September 19, the minister urged Indian startup companies to be careful against potential cyberattacks, geopolitical risks and other disruptions.
Addressing the media, the minister said that India’s emergence as a country capable of designing and manufacturing chips for semiconductor devices could improve its position in the global semiconductor value chain, potentially drawing attention from established players and opponents of India’s rise. He also stated that he had discussed these concerns with the industry and urged them to prepare for potential cyberattacks, threats, and other possible disruptions.
These risks could extend beyond common business competition to include cyberattacks, physical attacks, misinformation, and other forms of disruption. The country’s push for semiconductors has also attracted increasing investment interest. Recent announcements related to this include Applied Materials, a United States manufacturing company, planning a US$5 billion investment in India through 2035, Lam Research’s proposed ₹10,000 crore investment; and Fujifilm planning to invest approximately ₹800 crore to establish a semiconductor material plant in Dholera. These developments reflect the country’s growing ambition to expand India’s semiconductor ecosystem.
The warning from Union IT Minister reflects the major concern that needs to be cater by Indian semiconductor companies to consider cybersecurity and other broader disruption risks alongside investment in manufacturing capacity, technology and talent.
The post Vaishnaw Warns India’s Semiconductor Industry of Cyberattacks and Disruptions appeared first on ELE Times.
Vishay D2TO35S: 35 W Automotive Thick Film Power Resistor with Top-Side Cooling in TO-263 Package
Vishay Intertechnology has introduced a new Automotive Grade, top-side cooling mount thick film power resistor. The Vishay Sfernice D2TO35S is designed for automotive applications, offering improved thermal performance and reduced PCB space requirements. The resistor provides high power dissipation of up to 35 W at 25°C and is housed in a surface-mount TO-263 (D²PAK) package.
As thermal constraints increasingly become the primary system design limitation, many power components are transitioning from PCB-based cooling to top-side cooled architectures. By transferring heat directly to a heatsink, the D2TO35S released today enables up to nine times greater power dissipation than standard PCB-mounted devices when paired with an appropriate heatsink. Its compact, surface-mount design allows designers to increase power dissipation within the same footprint or provide the same functionality in a smaller footprint, while lowering PCB temperatures, reducing thermal stress on neighboring components, and improving overall system reliability.
Offering a non-inductive design for improved signal integrity and power handling in fast transient conditions, the D2TO35S features a resistance range from 4.7 Ω to 550 kΩ — with tolerances down to ± 1 % — thermal resistance of 4.28 °C/W, TCR down to ± 150 ppm/°C, and a wide operating temperature range from -55 °C to +175 °C. The RoHS-compliant device is solder reflow secure at 270 °C/10 s.
The post Vishay D2TO35S: 35 W Automotive Thick Film Power Resistor with Top-Side Cooling in TO-263 Package appeared first on ELE Times.
When AI agents make decisions, trust becomes infrastructure

AI agents are beginning to change something more fundamental than how organizations use software. They are beginning to receive authority.
A conventional AI system can provide information, summarize data, identify alternatives, or recommend an action. An agent can increasingly go further. It can select an action, execute it, commit resources, change a system, initiate a transaction, and modify an engineering workflow. And potentially make decisions without waiting for a human at every step.
That is a much larger transition than moving from one generation of software to another. It’s a transition from assistance-based AI to authority-based AI. And that raises a different question. It’s no longer enough to ask: What can the agent do?
Organizations must also ask: What authority should the agent have to make this decision? And immediately after that: What evidence and level of risk justify giving it that authority? As AI moves from providing information to making consequential decisions, trust can no longer remain an assumption surrounding the system. In other words, trust must become infrastructure.
From assistance to authority
Consider the following progression:
Assist → Recommend → Decide→ Execute → Commit
These are not simply increasing levels of AI capability. They are increasing levels of delegated authority. At the first level, AI provides information. At the second, it recommends what might be done. At the third, the organization allows it to select an action. At the fourth, it executes that action. At the fifth, it commits something consequential: money, inventory, production capacity, infrastructure, engineering changes, or contractual obligations.
The risk changes dramatically across that progression. A bad recommendation can be rejected. A bad decision that has already been executed may have to be reversed. Some actions may be expensive to reverse. Others may be impossible to reverse.
That creates a fundamental distinction: Capability determines what an agent can do. Trust determines what authority an organization permits it to exercise. Organizations therefore should not think only about whether an agent is intelligent enough to perform a task. They must think about the risk of giving it authority over the outcome.
Every decision has an authority boundary
An agent does not make a decision in isolation. It makes that decision because an organization has explicitly or implicitly allowed it to act within some boundary. That boundary matters. Can the agent spend $100? $100,000? Can it select a supplier? Can it change a production schedule? Can it modify a design? Can it release that design? Can it shut down infrastructure? Can it move capital? Can it enter a contractual commitment?
These are fundamentally different levels of authority. So, the important question is not simply whether AI can make good decisions. It is: Which decisions can be delegated, under what conditions, within what limits, and based on what evidence? That is an organizational architecture problem as much as an AI problem.
Agentic commerce example
An AI shopping agent can search far beyond the handful of websites a person would normally visit. That can be extremely valuable. For instance, a small retailer that previously had almost no chance of being discovered by a particular customer can suddenly compete because the agent evaluates the market rather than simply visiting familiar stores.
But the same capability creates another possibility. What happens when fraudulent merchants begin designing storefronts specifically to attract autonomous agents? The agent now must determine whether the merchant exists, whether the product is authentic, whether the offer is credible, whether fulfillment is reliable, and whether the transaction should be authorized.
The trust decision did not disappear when the human stopped shopping manually. The trust decision moved into the agentic infrastructure. Now extend the same problem into industry. The consequences become much larger.
Authority multiplies consequence
Imagine an agent selecting a supplier. Another changing factory production schedules. Another reallocating inventory. Another configuring computing infrastructure. Another executing financial transactions. Another modifying an engineering design. Another deciding whether that design has satisfied the conditions required to proceed.
Every one of these systems may be highly capable. But capability alone does not answer the most important organizational question: How much consequence should this system be allowed to create? This is why authority changes the risk equation.
The same model may be acceptable for recommending a decision but unacceptable for executing it autonomously. The difference is not necessarily intelligence. The difference is authority and consequence.
Trust has multiple layers
Trust infrastructure cannot be reduced to a model confidence score. An organization allowing autonomous decisions needs multiple layers of evidence and control.
- Identity: Which agent is acting, and on whose behalf?
- Provenance: What information, models, sources, and prior decisions support the action?
- Validation: Has the proposed action satisfied the required technical or business checks?
- Risk: What can happen if the decision is wrong, incomplete, manipulated, or based on incorrect information?
- Authority: Is this agent permitted to make this particular decision?
- Authority: Is this agent permitted to make this particular decision?
- Boundaries: How far can it act without additional approval?
- Traceability: Can the organization reconstruct what happened and why?
- Verification: Did the action produce the intended outcome?
- Accountability: Who ultimately owns the consequence?
These layers are interconnected. And more importantly, they should not remain constant as authority increases. Greater authority requires stronger trust infrastructure.
More intelligence doesn’t eliminate risk
This is particularly important as AI becomes more capable. Greater intelligence can improve decisions. But greater intelligence does not eliminate the underlying risk created by delegated authority. In fact, a more capable agent may be able to operate across more systems, make more decisions, execute them faster, and create larger consequences before a human intervenes.
That means more intelligence does not eliminate the need to manage risk. Greater capability can increase the amount of consequential authority that must be controlled. This is not an argument against autonomy; it’s an argument for matching autonomy to evidence.
The objective should not be to place humans permanently inside every decision loop. The objective should be to determine where autonomous authority is justified and where it’s not.
Evidence and authority must move together
This gives us a useful principle: Authority should expand only as supporting evidence becomes stronger. An agent may begin with recommendation authority. After repeated validated outcomes, it may receive authority to execute narrow and reversible actions.
With stronger evidence, the boundary may expand. More consequential decisions require stronger validation. Highly consequential or irreversible decisions require stronger evidence still. The progression becomes as follows:
Capability → Evidence → Risk assessment → Bounded authority → Decision → Execution → Verification → Accumulated evidence → Expanded authority
This is different from simply trusting an AI system because it performed well on a benchmark. Authority becomes something that is earned through evidence and bounded by risk.
Reversibility changes the evidence requirement
Not all decisions deserve the same trust threshold. Reversibility matters. If an agent makes a software configuration change that can be rolled back immediately, an organization may tolerate a particular level of uncertainty. However, if an agent commits millions of dollars, changes a physical manufacturing process, releases a production order, signs a contractual obligation, or sends a semiconductor design to fabrication, reversal may be extremely expensive—or impossible.
That produces another useful relationship: As consequence increases and reversibility decreases, the evidence required for autonomous authority should increase. This gives decision makers a more useful framework than simply asking whether AI should or should not be autonomous.
In other words, autonomy becomes conditional.
Speed makes trust more critical, not less
AI agents create another complication: speed. Speed is one of their greatest advantages. Agents can search alternatives, evaluate information, coordinate across systems, and execute decisions far faster than conventional organizational workflows. However, speed also compresses the opportunity to detect a bad decision before it becomes an action.
That makes the combination of speed plus authority particularly important. A human organization might take hours or days to progress from information to recommendation to decision to execution. But an autonomous system may traverse that sequence in seconds. If the decision is wrong, speed can turn one error into many actions before anyone recognizes what happened.
So, the faster autonomous authority operates, the less an organization can depend on after-the-fact human intervention as its primary protection. Trust infrastructure must increasingly operate at machine speed with identity, validation, risk boundaries, permissions, traceability, and verification. These attributes cannot sit outside the autonomous workflow; they must travel with it.
Trust can become an industrial advantage
This leads to an important competitive implication. Two organizations may eventually have access to comparable AI capability. Yet one may allow its agents only to recommend actions because it lacks the evidence, controls, and organizational confidence required for greater autonomy.
Another may have built sufficient trust infrastructure to allow agents to make and execute meaningful decisions within carefully defined boundaries. So, the second organization can potentially operate much faster. Not necessarily because its AI is smarter, but because it can safely grant the AI more useful authority.
That means competitive advantage may increasingly come from the combination of AI capability + evidence + risk control + bounded authority + execution speed. In other words, the model alone is not the complete system.
The next question for agentic AI
The first wave of generative AI largely asked: What can AI produce? Agentic AI introduced another question: What can AI do? And now the industry must confront the more consequential question: What decisions should AI be authorized to make?
And behind that question are two more questions: What evidence justifies that authority? What risk is the organization willing to accept when it delegates it? Those questions apply to commerce, finance, supply chains, manufacturing, infrastructure, and engineering. And eventually almost every environment in which autonomous systems can create real-world consequences.
The most capable agent will not automatically be the most valuable. The valuable agent will be one whose capability can be translated into trusted, bounded, and verifiable authority. That is the larger transition now beginning.
AI capability determines what becomes possible. Evidence establishes what can be trusted. Risk determines what must be controlled. Authority determines what the agent is allowed to decide. And when those decisions begin producing consequential outcomes at machine speed, trust becomes infrastructure.
Dr. Moh Kolbehdari is senior director of IC/packaging at Socionext US.
Related Content
- How to Plan Agentic AI Deployment for Chip Design
- Agentic AI Tackles RTL Verification’s Productivity Gap
- Why Microcooling Will Be a Critical Enabler of Agentic AI
- Agentic AI, Multi‑Physics, and Standards Will Redefine Chips Design
- The Magic of Agentic AI Will Come From a Holistic Approach to Chip Design
The post When AI agents make decisions, trust becomes infrastructure appeared first on EDN.
ROHM’s 2nd-Gen Terahertz Wave Oscillation Device Delivers 4 Times Higher Output Power
ROHM has developed a 2nd Generation terahertz (THz) wave oscillation device using semiconductor elements known as Resonant Tunneling Diodes (RTDs). The company is making the device available via the RTD-EVK-G2 Terahertz Wave Device Evaluation Kit, which includes a sample device, cable, and evaluation board. The kit enables companies and research institutions to evaluate THz wave oscillation and detection in a compact development environment.
Occupying the frequency region between radio waves and light, terahertz waves combine the penetrating properties of radio waves with the straight-line propagation of light. Because they exhibit unique absorption characteristics for polymers, moisture, and other substances, they are expected to be used in non-destructive testing without ionizing radiation, medical and healthcare applications, and high-resolution radar sensing. However, conventional terahertz systems require large equipment and high implementation costs, making it difficult for new companies and research institutions to enter the field or pursue commercialization.
Since the late 2000s, ROHM has engaged in joint research with the Institute of Science Tokyo, Osaka University, and many other universities and research institutions to develop THz wave oscillation and detection devices using RTDs. In 2024, ROHM began offering samples of 1st Generation products, achieving substantial downsizing and cost reduction compared with conventional methods.
What’s New in the 2nd Gen Wave Oscillation Device?To address the growing demand for improved signal quality in application development, ROHM has now developed a 2nd Generation terahertz wave oscillation device. The device maintains the same compact 0.5×0.5mm chip size as the 1st Generation product while adopting an internal structure that enables higher output power. As a result, output power has been increased to approximately 4 times that of the 1st Generation product, reaching a maximum of 40µW. The higher output power improves the detectability of THz waves after transmission through or reflection from target objects – making the device well suited for applications such as sensing and imaging that require high signal quality.
The device is mounted in the same 4.0×4.3mm PLCC package, maintaining the industry’s smallest footprint. This enables evaluation environments to be built even in space-constrained settings. In addition, compared with other THz generation methods, the RTD approach generates less heat and consumes less power. This reduces application development load at both companies and research institutions. Sales of the RTD-EVK-G2 evaluation kit, which includes samples of the 2nd Generation wave oscillation device, are scheduled to begin later this year at $3,300 per set.
By enabling evaluation at a lower cost than other methods, the kit supports the development of a wide range of applications. This includes non-destructive testing; imaging and sensing in the medical and healthcare sectors; material identification; and moisture detection. ROHM will also continue sales of 1st Generation devices for applications that prioritize low power consumption. For further information, please contact a sales representative or visit the contact page on ROHM’s website. Purchase of the evaluation kit requires signing a non-disclosure agreement (NDA) with ROHM.
Expanding THz Wave ApplicationsSharing his views on the development, Professor Safumi Suzuki, Laboratory for Future Interdisciplinary Research of Science and Technology, Institute of Integrated Research, Institute of Science Tokyo, said, “Terahertz waves are expected to be applied in a wide range of fields, including non-destructive testing, imaging and sensing, and wireless communications. At the same time, commercialization continues to face major challenges, such as the need for large-scale equipment and high implementation costs.
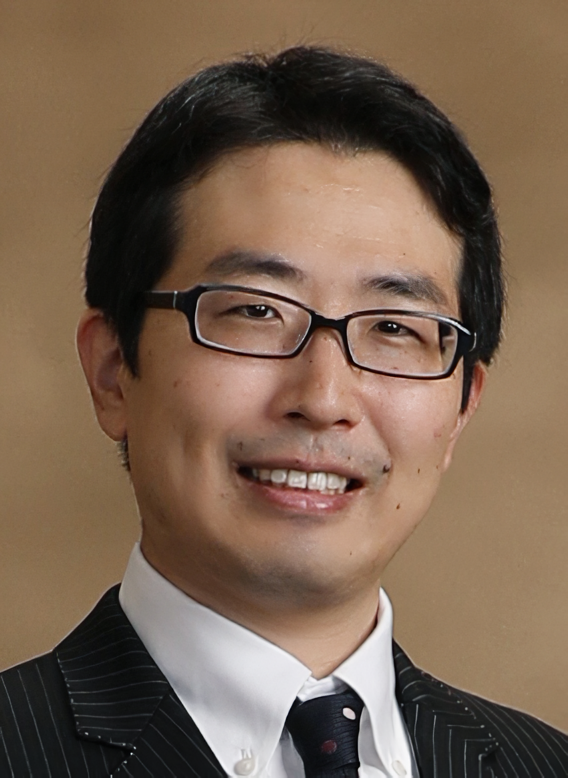 Professor Safumi Suzuki, Institute of Integrated Research, Institute of Science Tokyo
Conventional methods for generating terahertz waves include the ‘frequency multiplication’ method. This converts the frequency of an electrical signal into an integer multiple for output. The “photomixing” method that produces terahertz waves from the difference frequency created when two laser beams of different wavelengths are mixed in a photo-mixer. Both approaches necessitate large or medium sized costly equipment to generate terahertz waves.
“The RTD terahertz wave device, developed through many years of joint research with ROHM is compact, power saving, and does not require cooling. It can also be introduced at low cost, helping companies and research institutions begin terahertz wave research. With the launch of the 2nd Generation device featuring significantly improved oscillation output, I expect development of applications requiring higher signal quality to accelerate,” added Suzuki.
“With the launch of RTD-EVK-G2, we expect to make another major step forward toward the practical implementation of terahertz technology. Feedback from users of the 1st Generation device revealed strong demand for higher-output devices. With this 2nd Generation product, we have succeeded in increasing oscillation output to approximately 4 times that of the 1st Generation device while maintaining a compact size, bringing us closer to meeting those needs. Terahertz technology is steadily progressing toward real-world implementation,” mentioned Ken Nakahara, General Manager of ROHM Research & Development Center, ROHM Co., Ltd.
The Smallest Terahertz Wave Device Now Becomes Smarter!Innovative oscillation and detection devices have been ROHM’s forte. Readers will remember that last year, the company introduced the first generation of the industry’s smallest THz wave oscillation and detection devices utilizing RTDs. Its extremely compact size, typically less than one-thousandth that of conventional oscillators, enabled this innovation to ensure easy development of terahertz wave applications, even in space-constrained environments.
By positioning the antenna surfaces of the oscillation and detection devices facing each other 10mm apart, a dynamic range of 40dB (typ.) was easily achievable. Both oscillator and detector maintain a drive power consumption of 10mW (typ.), while their ability to oscillate and detect terahertz waves at room temperature eliminates the need for cooling equipment required with some conventional methods. These compact, power-saving devices are almost unaffected by the operating environment, enabling use in a wide range of applications.
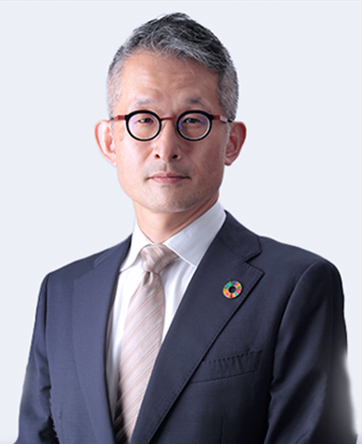 Ken Nakahara, General Manager of ROHM Research & Development Center
Going forward, ROHM intends to continue diversifying the possibilities for THz wave application development and contribute to the early commercialisation and real-world implementation of terahertz technology. This will help accelerate its deployment across a broad range of industries. “ROHM will continue working together with customers, partners, universities, research institutions, and government agencies to support the development of terahertz wave applications and contribute to the realization of a sustainable society,” averred Nakahara.
The post ROHM’s 2nd-Gen Terahertz Wave Oscillation Device Delivers 4 Times Higher Output Power appeared first on ELE Times.
Getting ready for 6G networks

As 5G-Advanced continues to roll out, bringing AI/ML integration, integrated sensing and communication (ISAC), RedCap, and non-terrestrial network capabilities, support for 3rd Generation Partnership Project (3GPP) Release 19 (R19) is emerging, setting the stage for initial 6G deployment and testing. Qualcomm Technologies, for example, is already incorporating AI/ML into RF modems to control real-time signal conditions, dynamic impedance matching, and predictive power scaling. Its latest X105 5G Modem-RF platform is 3GPP R19-ready.
 (Source: Adobe Stock)
Many of the technologies under consideration for 6G are already emerging in 5G-Advanced, giving vendors and operators an opportunity to trial capabilities such as AI-driven network optimization and ISAC before committing to broader 6G rollouts, according to ABI Research.
5G-Advanced rollouts are creating a practical runway toward early 6G deployment and testing. The September/October 2026 digital issue looks at how the industry is progressively validating the technologies needed for initial 6G interoperability and performance.
ABI Research provides an update on the transition from 5G to 6G. Research analyst Michael Moreno reports that 6G will embed AI deeper in the radio access network and core to manage radio resources, optimize performance, and deliver a more intelligent network. While AI already exists in 5G networks, 6G is designed to integrate AI capabilities more deeply into the network architecture, he said.
Although 6G is still being defined through the 3GPP standards process, Moreno said it is clear that AI, distributed computing, and sensing are becoming as integral as new frequencies, lower latency, and data rates.
5G, 5G-Advanced, and 6G networks all raise test challenges, particularly around uplink efficiency and modulation performance. This is why engineers are revisiting where power amplifier (PA) linearization should happen and how it should be validated, according to Andreas Oelemann, program manager of AI for wireless at Rohde & Schwarz: “PA linearity remains one of the hardest tradeoffs when designing wireless communication systems.”
Oeldemann reports that digital post-distortion (DPoD) is gaining some attention because, unlike conventional digital pre-distortion, DPoD shifts part of the compensation burden to the receiver. He discusses a hardware-in-the-loop testbed built around standard-compliant 5G signal generation and wideband signal analysis.
Two critical areas for wireless design are RF and timing devices. Contributing writer Stefano Lovati reports that sub-6-GHz and mmWave signal chains, higher front-end module integration, and gallium nitride PAs are shaping some of key design decisions on the road from 5G to 6G.
He also finds that RF digital front ends are integrating functions that were previously handled by analog parts. In addition, front-end architectures are beginning to include Frequency Range 3, AI, and early 6G interoperability as 5G-Advanced is rolled out.
The underlying timing infrastructure that keeps 5G networks synchronized has become a strategic technology domain, Benjamin Bunyatipanon, digital marketing specialist for Microchip Technology’s frequency and time system business unit, said. He explores why cesium clocks matter and how they fit into 5G timing architectures, with new challenges in synchronization, global navigation satellite system dependence, and critical-infrastructure reliability.
Also in this issue, we cover top 10 5G chips and modules introduced over the past year, targeting a range of applications, including smartphones, wearables, industrial IoT, and connected vehicles. Don’t miss the wireless chip roundup. These devices feature high integration, low power consumption, and advanced security features, driven in part by the need for multiprotocol functionality and edge AI applications.
Cover image: Adobe Stock
The post Getting ready for 6G networks appeared first on EDN.
UK launches Semiconductor Catapult to strengthen sovereign capabilities in AI hardware and defense
Tри освітні програми РТФ та ФБМІ КПІ ім. Ігоря Сікорського пройшли міжнародну акредитацію

Румунське агентство із забезпечення якості вищої освіти (ARACIS) акредитувало три бакалаврські програми КПІ та присвоїло їм європейський знак якості інженерної освіти EUR-ACE®:
Університетське управління, наука та міжнародна діяльність: КПІ ім. Ігоря Сікорського розвиває співпрацю з Естонією

🇪🇪 Ректор КПІ ім. Ігоря Сікорського разом із керівниками 12 українських університетів та представниками Міністерства освіти і науки України, зокрема заступником міністра Миколою Трофименком, Верховної Ради України та Національної академії педагогічних наук України відвідав Естонію з робочим візитом.
Openterface KeyMod: turning your smartphone into a control console
Openterface KeyMod is a pocket-sized USB bridge that turns a smartphone into a complete control console for computers, servers, kiosks, and embedded systems. The project comes from TechxArtisan and is available in two versions: Mini and Plus. TechxArtisan’s Crowd Supply campaign explains how it all works, and the hardware files are being released.
The device connects to the target machine over USB and presents itself as a composite device. It has an HID interface for keyboard and mouse, plus a USB network bridge called CDC-ECM. The smartphone runs the KeyCmd app, which talks to the KeyMod over BLE 5.3 in the Mini, or over wired USB in the Plus. The Plus version offers higher bandwidth, useful for heavier transfers.
How the network bridge worksThe network bridge assigns a fixed IP to the target, 192.168.11.2, and to the host, 192.168.11.1. This creates a private point-to-point network with no configuration needed. That opens a direct channel for SSH terminal sessions, file transfer, and other administration tasks. The BLE connection uses AES-128 encryption and ECDH P-256 key exchange, with support for authenticated pairing. Security is not an afterthought here, but a core part of the design.
The HID modes include keyboard, touchpad, gamepad, presentation, macro, and shortcuts. All of them are controllable from the KeyCmd app. In addition, an experimental AI mode called Agent Mode lets you plan and execute terminal commands, HID input, and macros through an LLM. The local model tested is a 0.6B Qwen, which sent 1,130 characters in under a minute. For those working with embedded systems, this means quick, direct control.
Size and technical specificationsThe KeyMod Mini measures 25 × 15 × 5 mm and weighs about 2.4 grams. The Plus is larger, at 44 × 20 × 10 mm, and weighs 8.9 grams. The BLE 5.3 module reaches 2 Mbps in wireless mode, while USB goes up to 10 Mbps. BLE range is about 5 meters under optimal conditions, up to 10 meters at most. The target gets a fixed IP and the network is ready to use within seconds.
At the heart of the device is a CH32 HID controller, alongside a BLE 5.3 Bluetooth module. The project’s open source philosophy invites you to explore and modify the code.
A single dongle turns your smartphone into a full console for IT administration, embedded development, and gaming. The open source philosophy and advanced features, like the network bridge and AI, make it a versatile tool. The firmware will be open source after the funding campaign, and OSHWA certification is planned. Hardware files are being released, so anyone who wants to can study and replicate the project.
The practical applications are many. A network administrator can manage a server remotely over SSH. An embedded developer can control a development board without opening a laptop. A gamer can use the smartphone as a wireless gamepad. The presentation mode also turns the phone into a slide remote. The possibilities grow with Agent Mode, which automates complex command sequences.
Battery life is not a concern, because the KeyMod draws power from the target machine’s USB port. Power consumption is minimal, and the device is always ready to go. The KeyCmd app is available for Android 5.0+ and iOS 17.0+, covering most modern smartphones. For those using a Raspberry Pi 5 as a server or development station, the KeyMod is an ideal companion for quick management. The direct USB connection removes the need for Wi-Fi or extra cables.
In short, the Openterface KeyMod is a project that combines compact hardware, open source software, and advanced features. The experimental AI mode opens up new possibilities for automation. OSHWA certification and the release of hardware files show a real commitment to the community. If you are looking for a practical way to use your smartphone as a work tool, this dongle deserves attention.
Source: https://www.crowdsupply.com/techxartisan/openterface-keymod
The post Openterface KeyMod: turning your smartphone into a control console appeared first on Open Electronics.
Arkansas Research Institute for Electronics Systems launched
Creating higher voltages, part 1: Voltage boosters

There are several ways to boost a relatively low AC or DC voltage by a factor of two or three, each with tradeoffs and constraints.
Lower-voltage circuitry dominates much of design and associated discussions, with ICs and systems operating from five, three, and one, and even sub-one volt rails. There’s good reason for this: in general, such circuits require less power and have lower dissipation than higher-voltage circuits. Further, these lower-voltage circuits also can operate at higher speeds since the voltage/current swings are smaller, and so the slewing demands (dV/dt, dI/dt) are also reduced.
However, there are many cases when a higher voltage is either preferred or mandatory. It’s interesting to see the creative ways that have been devised to develop a high voltage from a low-voltage source, often with techniques that are a hundred years old and still in use.
Why would you want to use a higher voltage, since lower operating voltages offer advantages of lower power consumption and higher speeds, among other factors? Among the reasons:
- First, a circuit may operate at a lower voltage, but need a higher voltage in one section to boost signal/noise ratio (SNR); this is common for sensitive front ends in RF and sensor applications.
- Second, when a circuit must deliver power – not voltage – to a load, it’s always more efficient to do so at higher voltages due to reduced losses (internal, switching, IR, and I2R). In these cases, it may be beneficial, even if not mandatory, to use a somewhat higher voltage. In a typical situation, a battery and regulator providing 3 V for the main circuitry may also need to provide a 12-V rail for a sensor.
- But the biggest reason is that requirement is simply unavoidable. There are many real-world applications where the voltage needed is determined by the physics of the situation, and there is no way to “get around” those requirements. For example, many scientific, medical, and test systems require higher voltages (>100 V to >1000 V) to set up specialized components such as vacuum electron devices (VEDs—the now-preferred designation for vacuum tubes) or create electric fields.
There are two very different ways to do increase a low voltage to a higher one: via a transformer, or via some type of switched-capacitor arrangement.
The transformer’s principle is simple and (hopefully) known to everyone reading this blog. An AC voltage on the primary (input) side is stepped up (or down) in proportion to the turns ratio between primary side and secondary (output) side.
For example, if the primary has 10 turns and the secondary has 100 turns – a 1:10 ratio – the voltage on the primary will be stepped up by a factor of ten (Figure 1). Of course, if you need a DC output, that ×10 AC output would need to be rectified and filtered. Use of a transformer to increase or decrease an AC voltage been known for about 150 years and is widely used to step up/down voltages in power-line installations, of course. However, it is often not the best choice for small circuits.

Figure 1 The relationship between primary (left side) and secondary (right side) turns ratio and voltage (and current) step up/step down is simple and a fundamental principle of magnetics. (Image source: Allelco)
However, while the transformer is very good at voltage step-up (or step-down) for larger systems, it is relatively large, costly, and heavy relative to a modest PC board. Further, it is not compatible with IC processes and packaging, and so would have to be mounted as a separate unit. Despite these drawbacks, it is sometimes still the right solution with respect to various tradeoffs.
The alternative is usually a circuit which uses some arrangement of switched capacitors. These clever schemes that have been in use for many years. They are often more practical and IC-compatible, because ICs can provide fast switching of the capacitors. Depending on their size, these capacitors can be in-chip or external; either way, a capacitor is more PC-board “friendly” in many cases than a transformer. These step-up approaches most commonly use a charge pump or a “flying capacitor” topology (where the capacitor is alternately switched or “flys” between input and output sides).
Charge pumps use an electronic switch to control the connection of a supply voltage across a load through a capacitor in a two-step process (Figure 2). in the first step, a capacitor is connected across the DC input supply, charging it to that same voltage. In the second step, the switches are used to reconfigure the circuit so that the capacitor is in series with the supply and the load. Now, the voltage across the load is doubled, as it is the sum of the original supply and the capacitor voltages. The switching action is repeated. Additional regulation is needed to smooth out the pulsed voltage at the output.

Figure 2 In the basic charge pump, the switching capacitor is charged from the input voltage to ground in the first phase, and then connected between the input voltage and output voltage; this “stacking” creates an output voltage which is twice the input voltage. (Image source: Texas Instruments)
An external or secondary clock circuit drives the switching, typically at tens of kilohertz up to several megahertz. A higher frequency minimizes the amount of capacitance required, as less charge needs to be stored and replenished in a shorter cycle. However, higher frequencies can also have higher losses, so there’s a tradeoff.
By adjusting the switching duty cycle, charge pumps can deliver double, triple, half, and scaled (such as ×3/2, ×4/3) ratios. With some rearrangement of the topology, they can also invert or reduce the output voltage (often called buck mode).
Charge pumps can be efficient (80-90%) but only when the components are sized for a specific load current. If the load current changes, the efficiency drops. Also, there are losses in the switching circuity which increase as the switching frequency increases; on the other hand, the output ripple is far less at higher frequencies, so the output filtering is simplified.
These pumps are widely available and used as standalone voltage-boost ICs, or as part of buck-boost regulator ICs. They are also often embedded within an IC to provide the higher voltages needed by some (not all) internal functions or external I/O (such as enabling a 3-V RS-232/423 interface IC to provide a 5-V or even 12-V drive. The capacitors are usually external to the IC.
The switched capacitor is just one of several related capacitor-based variations which use electronic switches to transfer charge between an input-side capacitor and an output-side capacitor. The charge pump is not the only option: there’s also the “flying capacitor” (Figure 3).

Figure 3 A capacitor can be switched from a voltage input to output capacitor and load, and the resulting charge transfer can provide voltage boosting as well. (Image source: Analog Devices)
The flying-capacitor principle is this: as the charge q in a circuit is unchanged (let’s assume that there is no load, for now) then the input-side charge q = C1 × V1. Then, if this charge is switched to another capacitor on the output side, q flows to that capacitor but is unchanged, and thus the voltage on the second capacitor changes, as q now equals C2 × V2. If the output-side capacitor is smaller than the input-side one, the output-side voltage will be higher than the input-side voltage.
This almost sounds like something for nothing, but it is not. As charge is “drained” from the output side by the load, the capacitor’s voltage will decrease. To correct this, the input-to-output action must be repeated at a high-enough rate to replenish the lost charge.
Incidentally, the flying-capacitor scheme was used many years ago to provide galvanic isolation between a sensor and a circuit. The sensor for be on the “input” side, while the circuit would be on the output side. The voltage across the sensor would be captured and then transferred to the system circuitry without any ohmic path between the two sides. This scheme has largely been made obsolete by modern isolation schemes using transformer, capacitive, optical, and even RF coupling.
In theory, the transformer or switched-capacitor schemes can be used for transforming, say, 10 or 100 V to thousands of volts. However, in practice, they cannot be used without major adjustments, as the high-voltage world has some unique issues.
However, as voltages go beyond about 60 V, issues of safety and regulatory mandates become a concern. As these voltages reach into the hundreds and thousands of volts, there are additional unavoidable and non-intuitive issues of material characteristics and electrical phenomena that show that design and construction for these voltage levels is a very different world.
Part 2 of this blog will look at how clever schemes based primarily on diodes and capacitors are used to develop those much-higher voltages using voltage multipliers.
References:
- Flyback converter, Wikipedia
- Cockcroft-Walton voltage multipliers, Wenzel Associates (via TechLib)
- Charge Pumps: The Forgotten Converter, Texas Instruments
- Switched Capacitor Voltage Converters, Analog Devices
—Bill Schweber is a degreed senior EE who has written three textbooks, hundreds of technical articles, opinion columns, and product features. Prior to becoming an author and editor, he spent his entire hands-on career on the analog side by working on power supplies, sensors and signal conditioning, and wired and wireless communication links. His work experience includes many years at Analog Devices in applications and marketing, and he also developed significant mechanical-engineering insight while designing control electronics for large materials-testing systems.
Related Content
- High-Voltage Design: Living Long and Still Prospering
- Pulsed high-power systems are redefining weapons
- Learning to like high-voltage op-amp ICs
- Rich voltage, poor voltage: My incandescent tale
The post Creating higher voltages, part 1: Voltage boosters appeared first on EDN.
Eaton to use Infineon’s silicon carbide power devices in medium-voltage solid-state transformer for 800V data-center power distribution
GSM remote control: the GSM Shield for SIMCom and Quectel modules (part 1)
We emulate the TDG series remote controls using the GSM Shield.
It was not long ago that we presented our GSM shield for GSM/GPRS modules from SIMCom, QUECTEL, FIBOCOM and others, designed to be embedded in Arduino-based projects that involve cellular connectivity; now the time has come for the first practical application, which in this specific case means replicating the operation of the TDG133 bidirectional GSM remote control, published back in issue no. 148 of July 2010, which lets you manage two relay outputs and two voltage-level inputs. For the occasion we developed a set of commands useful for setting the basic functions both by sending SMS and by sending commands through the serial monitor of the Arduino IDE. Both the electronics and the firmware development are based on the Arduino Mega 2560 or Fishino Mega 2560 board. This is for reasons of available Flash and SRAM memory for the application, but above all for the availability of free I/O pins for developing the project.
The platform on which we will develop our application is the Arduino Mega 2560, widely supported by the GSM shield, since it is the only one able to provide the set of I/Os needed to manage the input and output signals; specifically, the application proposed here requires:
- two I/Os to manage the digital outputs, at least in the basic application, though the project supports up to eight digital outputs and therefore considers the use of eight I/O lines;
- two I/Os to manage the digital inputs, which can be configured to work as active high, active low or on change; in reality up to eight input lines are made available;
- as for the indicator LEDs, those already present on the GSM demo board are used.
For the operating logic we refer to the TDG133 remote control, whose functions we will replicate as far as the available hardware allows. Let us recall that the TDG133 is a bidirectional remote control module that lets you check remotely the state of two relay outputs, in bistable or monostable mode, by sending suitable SMS messages completed with a password. It also lets you acquire the state of two optoisolated inputs.
The commands can come from telephone numbers stored in a list of a maximum of eight numbers, to which the device sends SMS messages and voice calls when it considers the digital inputs to be triggered, based on the settings made during configuration. The TDG133 remote control can also work as a gate opener, a mode to which up to 200 telephone numbers can be associated.
Hardware block diagramOnce we have established what the TDG133 did, we also know what our project has to do, since it must emulate that system using Arduino or compatible hardware. The block diagram in Fig. 1 gives an idea of the electronics our GSM Shield-based remote control is made of.
Like the TDG133, this remote control also provides two digital inputs and two relay outputs. In our application we make available up to eight digital inputs, which can be active high or low, and eight digital outputs useful for driving up to a maximum of eight relays; in reality this availability is hardware, because the current firmware of the Arduino Mega 2560 only allows two digital inputs and two digital outputs to be managed, and anyone who wants to use all 8 lines will have to work on the code.
 Fig. 1 Hardware block diagram.
The block diagram highlights the logic with which the application was developed.
- The Shield Telecontrollo board, highlighted with a green square, is mounted on the GSM Shield, which in turn is plugged into the Arduino Mega 2560.
- The Shield Telecontrollo provides up to eight digital inputs and, by means of board-to-board jumpers, it is possible to select whether the input is active at logic high, in which case the pull-down must be inserted, or active at logic low, in which case the pull-up must be inserted. The event can be generated by bringing the desired input to GND or to +5Vdc. To do this you can use the usual laboratory jumper wires such as code “7300-JUMPER50”.
- The Shield Telecontrollo provides up to eight digital outputs with which the boards with two, four or eight relays can be controlled; these boards all mount relays with a +5V coil voltage. In this case we refer to the products “2846-RELAY2CH”, “2846-RELAY4CH” and “2846-RELAY8CH”. Jumper wires must also be used to connect the relay boards.
- Power to the Shield Telecontrollo can come either from the Arduino Mega 2560 via a USB type B cable, or from the micro-USB socket of the GSM Shield, via a micro-USB cable.
- The connection via USB type B cable also allows the Arduino Mega 2560 board to be programmed, as well as sending the configuration commands through the serial monitor of the Arduino IDE. Through the monitor you can also receive information on the state of the events intercepted during operation, SMS sending and receiving, etc.
- If you want to monitor the AT commands sent by the Arduino Mega 2560 to the GSM module, you can use the usual USB/TTL converter (code FT782) connected to the special connector present on the GSM Shield. The FT782 electronics also allow 5Vdc power to be brought to the GSM Shield.
The circuit diagram of the GSM Shield has already been published in issue no. 231, so here we will only describe the circuit of the Shield Telecontrollo, whose circuit diagram is shown in these pages; it is something very simple that takes the connections of port PA0÷7 of the Arduino Mega 2560 and, via on-board jumpers, distributes them for managing the digital output lines used to drive the relays. It also takes the signals of port PL0÷7 of the Mega 2560 for managing the digital input lines. These lines are all on the 36-pin connector (18 pins x 2 rows) of the Arduino Mega 2560, to which the six LEDs mounted on the Shield Telecontrollo and intended for general purposes are also connected (Port PC0÷7).
As for the digital inputs, it is possible to set whether they must be active with a high or low logic level. The operating mode is selected via jumpers (J1÷8), and in particular if the jumper is inserted in position 1-2 the 10 kohm pull-up resistor is inserted and therefore the input is active low, while if the jumper is in position 2-3 the 10K pull-down resistor is inserted and therefore the input is active high.
For each input a contact point has been provided on connector CN5, to be used, via jumper wires, to activate the corresponding input, that is +5V if active high or GND if active low. We have therefore provided two more connectors of 8 poles each, labelled CN1 and CN2, to which we have brought the +5Vdc and GND lines respectively. In this way, for each of the eight inputs there is a corresponding +5Vdc or GND point to be used for simulating the change of state on the input.
As for the outputs, these have simply been brought to connector CN4 together with the +5V and GND lines needed to power the auxiliary relay boards to be used for this application.
To complete the demo board we have also brought out the free lines present on the many other connectors of the Arduino Mega 2560, so as to give the end user the possibility of using the function associated with them. All the lines already occupied for managing the GSM board are not brought out.
In order to make the demo board more versatile we have also provided a section on the PCB that acts as a prototyping development area where users can mount components of their choice to develop their own applications. The pitch between one pad and the next is the usual 2.54mm. This area provides over 315 single pads free of potential, plus a smaller set of pads to which the +3V3, +5V and GND lines have been brought.
 Fig. 1 Hardware block diagram.
 PCB layout of the Shield Telecontrollo.
For the project you need to prepare the Shield Telecontrollo, that is, make the relevant printed circuit board starting from the copper-side traces available for download together with the project files. During the assembly of the few components present, it is advisable to start with the 0603 SMD resistors and then move on to the 3-pole jumper connectors, followed by connectors CN1, CN2, CN4 and CN5. Finally, mount and solder the board interfacing connectors, namely CN3, CN6, CN8, CN10, CN12, CN14 and CN15.
With these, the assembly of the prototype board is complete; all that remains is to mount it on top of our GSM board and move on to implementing the sketch to be loaded into the ATmega 2560 microcontroller of the Arduino Mega 2560.
Assembly plan
Component list:
- R1, R2, R3, R4, R5, R6, R7, R8, R9, R10, R11, R12, R13, R14, R15, R16: 10 kohm (0603)
- CN8, CN10, CN12, CN14, CN15: 8-way Arduino strip (5 pcs.)
- CN6: 10-way Arduino strip (1 pc.)
- CN3: 2×18-way Arduino strip (1 pc.)
- CN1, CN2, CN5: 8-way male strip (3 pcs.)
- CN7: 10-way female strip (1 pc.)
- CN9, CN11, CN13, CN16: 8-way female strip (4 pcs.)
- CN4: 10-way male strip (1 pc.)
- J1, J2, J3, J4, J5, J6, J7, J8: 3-way male strip (8 pcs.)
- Miscellaneous: jumpers (8 pcs.), printed circuit board, the sketch
The architecture our application is based on makes use of the EEPROM built into the ATmega 2560 to store a set of parameters, including the SMS messages to be sent in the event of an alarm, and of the SIM memory, inserted in the GSM module, to store the phone numbers authorised to manage the remote control system.
We made this distinction because, although it is quite large, the EEPROM of the ATmega 2560 is not big enough to store all 208 phone numbers that the remote control can handle. We therefore decided to use the memory provided by the SIM to store the phone numbers in the phonebook, together with their description, just as you do on ordinary mobile phones. This approach also gives us the opportunity to show how to use the library functions created for handling the AT commands needed to read, write or delete the phonebook.
Two sketches in a single fileWith that brief introduction out of the way, we can start describing how the sketch containing the remote control management code is structured. First of all, note that the code actually contains not one but two sketches, which obviously do not run at the same time. This is possible thanks to a compiler directive that lets us choose whether to use the code that programs the factory parameters into the EEPROM of the ATmega 2560 or whether to activate the remote control management code. The directive that lets us select which sketch to run is the following:
#define WRITE_DEFAULT_DATA_EEPROM
This directive is found at the top of the file “GSM_TDG133.ino”. When this directive is commented out, the remote control code is compiled and executed; otherwise, the code that programs the default parameters into the EEPROM memory is compiled and executed. The parameter programming code does not reset the phonebook on the SIM inserted in the GSM module. Deleting any phone numbers present in the phonebook is done by sending specific command strings, which are interpreted and handled by the remote control code, which in turn sends the appropriate AT commands to delete one or all of the contacts on the SIM.
The EEPROM mapThe code that handles programming the factory parameters into the EEPROM is found in the file “_SetupEeprom.ino”, where at the top we find, in table form, the map of the EEPROM memory showing where the data is stored and how much space it takes up.
This map is designed to handle the text of the two input alarms (Input 1 and 2) and their related management parameters, as well as enabling/disabling SMS sending to the first eight numbers in the phonebook. Let’s look at the map in Fig. 2. As you can see, there is room left to add new text messages in case you decide to expand the input section from two to eight inputs in total.
 Fig. 2 Contents of the EEPROM memory.
Fig. 3 shows the flow chart of the EEPROM programming sketch, with the steps described below in sequence:
- Using dedicated library functions, the starting addresses in EEPROM are obtained for handling the PIN, PUK, etc. codes used by our GSM module library; looking at the EEPROM map table, you can see that these codes are at the top.
- This is followed by another library function to enable the serial port used for debugging. That is, the serial port that lets you, through the Arduino IDE serial monitor, receive a series of information from the running sketch and possibly send command strings to the sketch.
- Before setting the default values, a function is executed that resets the contents of the EEPROM memory, that is, it sets to 0x00 all memory locations that hold a value other than zero.
- The setting of the factory parameters then begins with writing the PIN, PUK, etc. codes.
- This is followed by the function that stores the system password (default value “12345”).
- This is followed by saving the flags.
- Finally, the strings used for sending SMS messages are stored.
- The system waits two seconds and then performs a full read-back of the whole EEPROM to verify that its contents match the factory values just programmed; first the default parameters are printed on the serial monitor in string format with a short description of the contents, followed by a read-back of the EEPROM and its printing on the serial monitor in hexadecimal + ASCII format.
 Fig. 3 Flow-chart of the system firmware.
As you can see in Fig. 2, at the top of the EEPROM contents are the PIN, PUK, etc. codes needed by our GSM library, followed by the system password (EEPROM starting address: 0x0050). Finally, the strings to be used for sending SMS messages are shown. Below the data shown, the entire contents of the EEPROM memory are then reported, from address 0x0000 up to address 0x0FFF. Now, if the directive:
#define WRITE_DEFAULT_DATA_EEPROM
is commented out, the main sketch containing the remote control code is compiled and executed, and we will now analyse it.
Initialisation: void setup()Let’s go back to the flow diagram in Fig. 3 and study it starting from the “void setup()” function, which is used to initialise the GSM library and to pre-load into memory a series of parameters stored in EEPROM. So during initialisation:
- using dedicated library functions, the starting addresses in EEPROM are obtained for handling the PIN, PUK codes used by our library;
- timer 5 is configured, used by the sketch to handle time variables such as the timers used for debouncing the digital inputs, timeouts for handling waiting times, etc. (the time base used for the timer is 2 ms);
- the digital inputs used to implement the sketch are configured;
- the digital outputs used to implement the sketch are configured, as well as the digital outputs used by the GSM library to handle the LEDs connected to it;
- the test routine on the LEDs present on the GSM Shield is executed;
- the interrupts used by the GSM library for its correct operation are set;
- the UART interface used for debugging via the Arduino IDE Serial Monitor is enabled and configured;
- the UART interface used for sending AT commands to the GSM module is enabled and configured;
- the GSM module is powered on and the state machine needed for its correct management is started.
This is followed by reading from EEPROM the parameters used in the sketch, such as:
- system password; default value “12345”;
- system flags, including enabling alarm notification SMS messages and related voice calls;
- inhibition times for the digital inputs;
- observation times for the digital inputs;
- maximum number of SMS messages to send in the event of an input alarm;
- phone number to which ECHO SMS messages are sent;
- gate opener function timeout.
Also during initialisation, the initial state of the alarm digital inputs is set, along with the setting of all the state machines used to manage the sketch and its related functions. Once initialisation is complete, the system enters main and the contents of the “void loop()” function are executed endlessly.
The main loop: void loop()The following are therefore executed:
- reading the state of the alarm digital inputs and their debouncing;
- handling the functions associated with the alarm digital inputs;
- handling the digital outputs used to control the relays;
- handling the state machines related to the GSM library, both during the GSM module initialisation phase and during normal operation for sending the AT commands needed for the sketch to work.
All the functions and state machines that manage every feature offered by the remote control system follow:
- commands for configuring the remote control system sent through the serial monitor;
- commands for configuring the remote control system sent by SMS;
- sending SMS messages according to the event that was logged;
- placing a voice call according to the event that was logged;
- handling the ECHO function, if enabled;
- handling the gate-open functions;
- handling the LEDs according to the event that was logged.
In detail, let us examine how the function “void ProcessStateMachineGsm(void)” works. At the top of the function we have the code, already used in the past, for managing the GSM library and its features, which, through an “if – else” conditional construct, determines whether it is running the initialization of the GSM module or whether it is up and running and therefore ready to process the AT commands sent by the sketch to the GSM module. So, looking at the block diagram, if initialization is running, all the code downstream of the conditional block will not be executed.
Once initialization is complete, the process can then move forward and process the library functions for handling the AT commands needed by the sketch, plus all the other functions needed to build the application under examination. Below is the code that distinguishes the initialization process from the steady-state process:
Gsm.ExecuteUartState(); if (Gsm.GsmFlag.Bit.GsmInitInProgress == 1) { Gsm.InitGsmSendCmd(); Gsm.InitGsmWaitAnswer(); } else { Gsm.UartContinuouslyRead(); Gsm.ProcessUnsolicitedCode(); Gsm.GsmAnswerStateProcess(); **** User code used to develop the sketch **** }
As you can see, the “if – else” construct contains a series of library function calls, one of which is always called because it sits outside the “if – else” construct, namely “Gsm.ExecuteUartState();”, which handles the state machine of the serial communication between the Arduino Mega 2560 and the GSM module mounted on the board. The other functions depend on the value taken by the flag “Gsm.GsmFlag.Bit.GsmInitInProgress”. Part of the user code, depending on what has to be done, can be placed inside the “else” section. Usually you put there all those functions that need to send an AT command to the GSM module and therefore must necessarily be executed once the system has reached steady state and not before.
Registering the first phone numberLet us continue with the analysis of the flow chart; once initialization has been passed, we find ourselves having to handle a series of possible situations, including the first incoming voice call for registering the first phone number in the list. On startup, the sketch scans the SIM phonebook looking for a valid phone number in the first memory location. If it finds nothing, for five minutes it waits for an incoming voice call, from any number, which will be registered in the phone book as “ADMIN”.
It is not mandatory, but it is always good practice to register a phone number in the phone book paired with a descriptive text, because when you receive SMS messages or incoming voice calls the GSM module will automatically return a text string starting with “+CLIP” to tell us whether the phone number is present in the phone book or not. If the string, in addition to the phone number, also contains the paired description, we have confirmation that this number is registered. With this information it then becomes easy to establish which memory location the number is in, to understand whether it is one of the first eight or whether it is instead one of the phone numbers with gate-open function only. Receiving an “Unsolicited Result Code” from the GSM module depends on the type of configuration that our library adopts during module initialization, otherwise such information would not be received (AT+CRC and AT+CLIP commands).
The yellow LEDs LD6 and LD7 blink alternately while waiting for the first incoming voice call. If the five minutes expire before a voice call arrives, the system enters steady state and, to configure the phone numbers in the phone book, you will use dedicated string commands to be sent either by SMS or through the serial monitor.
Generic and specific AT commandsOnce the test on the need to wait for the first phone number has been passed, the system finds itself processing functions whose purpose is to send AT commands to the GSM module under certain conditions. Let us see which ones: the general-purpose AT commands sent continuously to the GSM module with a one-second pause between one command and the next. These AT commands are meant to acquire a series of pieces of information from the GSM module, which are useful to the system for its operation. The flow can be interrupted when events occur, such as an alarm or something else, that require other, higher-priority AT commands to be sent. The generic AT commands used are:
- AT+CREG → GSM network registration information;
- AT+CSQ → GSM signal quality information;
- AT+CPAS → GSM module status information (used to know whether it is busy or not);
- AT+COPS → telephone operator information;
- AT+CPMS → incoming/outgoing SMS storage preferences;
- AT+GMI → information on the GSM module manufacturer;
- AT+GMM → GSM module model information;
- AT+GMR → information on the FW revision loaded in the GSM module;
- AT+GSN → IMEI code;
There are also specific AT commands sent following the sending of command strings. For example:
- AT+CPBR → AT command for reading a memory cell of the phone book;
- AT+CPBF → AT command for searching for a phone number in the phone book;
- AT+CPBW → AT command for writing/deleting a phone number in the phone book;
- AT+CMGD → AT command for deleting an SMS from the SIM memory.
Next comes the portion of code for handling the command strings needed to configure the remote control system, sent both from the serial monitor and by SMS. The sendable strings (which we will present shortly) are the same regardless of whether they are sent through the serial monitor or by SMS. After that we have a series of conditional blocks in order to check whether particular functions made available by the sketch should be executed if properly configured and enabled. In particular we have:
- sending, if enabled, of the SMS at system power-up (power return); this feature must be enabled by a dedicated command string and the SMS content can be the default one in EEPROM or a string programmed by the user through a dedicated string command;
- sending, if enabled, of the start-up SMS; this feature must be enabled by a dedicated command string; the content can be the default one stored in EEPROM or a different string programmed by the user through a dedicated string command;
- sending of alarm SMS messages according to the state of the digital inputs; the content of the SMS to be sent can be configured by users through a dedicated string command; alarm SMS messages can be sent only to the first eight numbers in the phone book, provided the number has been enabled to receive such an SMS (besides sending an alarm SMS to the first eight numbers in the phone book, the system, if enabled, can also place a voice call to those numbers if they are enabled);
- sending of a report SMS containing the state of the inputs and outputs (this feature must be programmed);
- – enable/disable the function with a dedicated command string;
- – set how often the report SMS must be sent;
- – the message is sent only to the first number in the phone book;
- sending of ECHO SMS. If this function is enabled, all received SMS messages that have no relation to the command strings used by the remote control system will be sent to a previously selected number in the phone book;
- sending of reply SMS messages to command strings sent by SMS;
- finally, the functions for processing incoming SMS messages and any incoming voice calls follow.
What has just been described is the backbone of the sketch we have built, which, as usual, is split into several files, described below.
- GSM_TDG133 → main file containing all the variable and constant declarations, compiler directives, string commands stored in the microcontroller Flash memory together with their unique numeric codes, the text strings used for printing to the serial monitor, and so on, as well as the functions “void setup()” and “void loop()”.
- AT_CmdFunction → file containing the code that handles the generic AT commands used in the sketch and manages the functions of the GSM library;
- DigitalInput → file containing the code for handling the digital inputs;
- DigitalOutput → file with the code for handling the digital outputs (relays);
- OutComingSmsVoc → file with the code for handling outgoing SMS messages and voice calls;
- ProcessStringCmd → file containing the code that decodes the string commands received from the serial monitor or via SMS;
- SerialStringCmd → file with the code for handling the strings received from the serial monitor or via SMS;
- TimerInt → file containing the code for handling TIMER 5, used for the time variables the sketch needs;
- _SetupEeprom → file containing the code that handles programming the factory configuration of the EEPROM.
Splitting the code across several files also keeps it tidier and lets it be divided into well-defined sections.
ConclusionsWell, that is all for now; in the next and final instalment we will look more closely at the programming aspects, explain how to use the commands and their syntax, and finish by describing the indications given by the LEDs on the GSM Shield.
Related products- GSM/GPRS SIM900 Shield for Arduino
- Pack of 50 Female-to-Female Jumper Wires – Assorted Colours
- 2-Relay Module 5 Vdc 10A (assembled)
The post GSM remote control: the GSM Shield for SIMCom and Quectel modules (part 1) appeared first on Open Electronics.
Navitas awarded ALATTIS US Army project to develop 10kV power semiconductors
Firehat: Bringing FireWire to the Raspberry Pi 5
Firehat is an open-source HAT that brings native IEEE 1394 FireWire to boards such as the Raspberry Pi 5 and the Radxa ROCK 2F. It adds an i.LINK/DV port to modern SBCs, eliminating the need for older computers. The board uses the VIA VT6315N controller and connects through the 40-pin GPIO header and the PCIe FFC connector. In this way, Firehat becomes a bridge between the DV world and digital storage.
The project solves a real problem: MiniDV and HDV camcorders use FireWire, but modern computers no longer have that port. Firehat fills the gap with a compact, open-source solution. The board measures 56 x 70 x 12 mm and weighs just 25 grams. It costs $79, a reasonable price for anyone who needs to digitize precious tapes.
How Firehat worksFirehat uses two separate connections on the SBC. The 40-pin GPIO header provides power and handles the OLED, buttons, LEDs, and buzzer. The PCIe FFC connection, on the other hand, carries FireWire data between the VIA VT6315N controller and the board. On Linux, Firehat appears as a standard PCIe FireWire controller, using the kernel’s FireWire stack.
DV capture is handled with open-source tools such as dvgrab and dvcont, or with the Equip-1 software stack for a standalone recorder interface. FireWire device control allows you to play, stop, rewind, and trigger captures via software. In addition, libavc1394 support enables reliable communication with camcorders.
For those who want to build the project themselves, you need an SBC with a PCIe FFC connector. The board with the Raspberry Pi 5 is the most common choice, but the Radxa ROCK 2F also works well. Firehat also includes a 1.3-inch OLED display and SK6812 RGB LEDs for status. Everything mounts in a compact case with accessible connectors.
 Firehat + Radxa ROCK 2F connected to a camcorder via FireWire
MiniDV, Digital8, DVCAM, DVCPRO, and HDV camcorders record to tape. Without FireWire, recovering those videos is a nightmare. Firehat lets you capture the digital DV stream directly to local storage without any quality loss. The DV stream is already digital, so no analog conversion is needed.
The project is designed for makers and archivists. Thanks to Linux support, captures can be automated with scripts. For example, you can rewind the tape, start recording, and stop at the end, all from the command line. Additionally, a 128×64 OLED display shows capture status in real time.
Firehat is not just an adapter; it is a true FireWire controller. The VIA VT6315N chip handles the IEEE 1394 protocol at the hardware level, while the software takes care of the rest. The 30 cm PCIe FFC connection ensures flexibility in mounting. The result is a stable and fast board, suitable even for long capture sessions.
What you need to get startedTo use Firehat you need only a few items. Here is the essential list:
- An SBC with a PCIe FFC connector, such as the Raspberry Pi 5 or Radxa ROCK 2F
- Firehat with VIA VT6315N controller and OLED display
- A FireWire camcorder with DV or HDV tape
- Linux with FireWire stack and dvgrab, dvcont, or Equip-1 tools
Assembly is simple: connect Firehat to the GPIO and the PCIe FFC, then boot the SBC. On Linux, the controller is recognized automatically. Finally, run dvgrab to start capturing. No hardware modification to the camcorder is required.
Firehat is available for $79 and the design is open-source, so you can also study the project. An SPI 256×64 OLED display can be added for richer interfaces, but the included 1.3-inch one is enough for most uses. The board is robust and well documented.
In conclusion, Firehat is the modern solution for those with legacy camcorders who want to save their footage. It combines open-source hardware, Linux software, and an accessible price. For anyone working with video archives, it is an indispensable tool.
Source: https://github.com/computerequipmentgroup/firehat
The post Firehat: Bringing FireWire to the Raspberry Pi 5 appeared first on Open Electronics.
Сторінки